CVEOCT 1810m
CVE-2026-111998 — Vanus: the Hardcoded `admin` Token That Owns the Cluster
A hardcoded admin token in Vanus grants cluster-admin to anyone who guesses it.
- #Vanus
- #DefaultCredentials
- #CWE-1392
Root cause first. Public advisories, patch diffs, and the detection gaps that survive the patch.
CVE Research
Root cause first. Public advisories, patch diffs, and the detection gaps that survive the patch.
A hardcoded admin token in Vanus grants cluster-admin to anyone who guesses it.
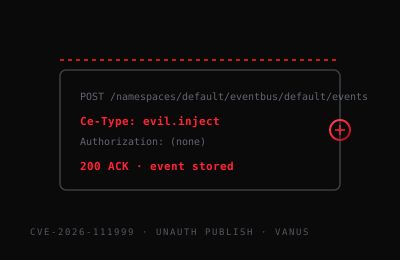
Unauthenticated CloudEvents publish on Vanus gateway port 8081.
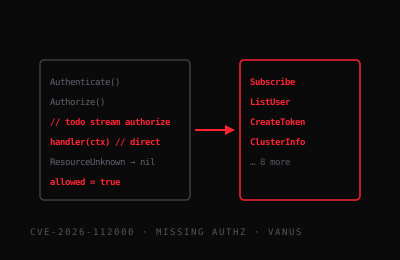
Missing authorization in Vanus gateway streaming RPCs and default-allow policy.
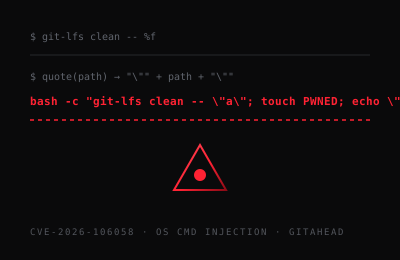
OS command injection in GitAhead Filter.cpp via unquoted filenames handed to bash -c.
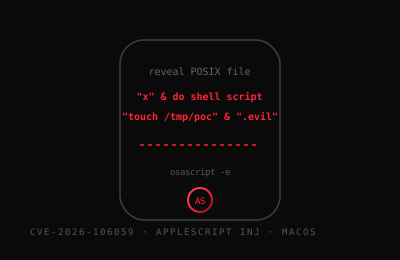
AppleScript injection in GitAhead ShowTool on macOS via unescaped filenames.
Unverified update installation and a persistent TLS bypass in GitAhead 2.5.0-2.7.1.
Stored XSS in httpdbg via a javascript: URL scheme that survives Mustache HTML-encoding.
No index is complete without the next one.
The dispatch carries one long-form writeup, roughly twice a month. Same standard, same lab, no drip feed.